AI writes.
We secure.
15 providers find leaked keys, open RLS, exposed database ports, CORS gaps, and missing rate limits. Get a Ship/Block verdict with AI-ready fix prompts.
Free URL scan. Anonymous results show one finding, with description and impact, and a locked fix prompt. A URL-only scan cannot see RLS policies such as USING (true). Supabase or Firebase connect is optional and read-only.
15
Security checks
100+
Secret patterns
AI
Security review
$0
To get started
How it works
Deeper than a URL scan.
Enter your URL
We fetch your app's HTML and JavaScript, scan for exposed secrets, check HTTP headers, and query OSV for dependency CVEs.
Connect your backend
Link Supabase or Firebase. We analyze every RLS policy, parse Firestore rules, check auth config, and audit storage buckets.
Get fix prompts
Copy-paste one universal fix prompt per finding. Pastes into Cursor, Claude Code, Lovable — any AI coding tool. Fix in seconds, not hours.
Security checks
15 checks. One score.
Every scan runs these checks in parallel. Results in about 1–2 minutes. Larger or slow targets can take longer.
Secrets & API keys
AI keys (OpenAI, Anthropic, xAI, Gemini, sb_secret_), payments, cloud, DBs
Backend data rules
Supabase RLS + Firebase rules — catches USING(true) and allow write: if true
Auth & access control
Unprotected endpoints, CSRF, cookies, CORS, rate limit, IDOR
Active DAST
XSS, IDOR, Next.js middleware bypass, unauthenticated MCP, open buckets
JavaScript analysis
Source maps, DOM sinks, client-bundled secret env, leaked system prompts
Infrastructure
TLS version + cert + DNS SPF/DMARC + 23-port network probe
Dependencies
CVE scanning via OSV for every JS/npm dep in the bundle
Payments
Stripe keys in HTML, unsigned webhooks, test-key leakage
MCP security
Tool poisoning, overpermissioned FS, rug-pull drift, exfiltration
Compliance
GDPR consent + privacy policy + hardcoded secrets in IaC files
Automated security monitoring
Scheduled re-scans at your chosen frequency. We monitor your production headers, check for newly discovered CVEs in your dependencies, and track configuration drift. Email and Telegram alerts the moment a new vulnerability hits your app.
Site Crawler
Discovers every page, API endpoint, and form on your domain. Scans the full attack surface, not just the homepage.
Telegram Bot
Scan via /scan command, get results + PDF in chat. Create support tickets with /support.
Automated Re-scans
Daily, weekly, or monthly. Catch regressions after every deploy.
Email + Telegram Alerts
Instant alerts on score drops, critical findings, and downtime. Choose your channel.
Vercel Deploy Gate
Auto-scan on every Vercel deploy. Block insecure code before it reaches production.
The problem
USING(true) = RLS "enabled" but database fully open.
The policy
RLS: enabled
Policy: USING (true)

The toggle is on.
The table is still open.
What Sekrd reports
⚠ CRITICAL: users table
  Policy: USING (true)
  → Anyone with anon key
    can read ALL user data

  Fix: USING (auth.uid() = id)
Why Sekrd
Sekrd vs. the rest
See it in action
What you get
BLOCK
3 critical issues
SHIP
All issues fixed
Binary verdict. Critical finding = BLOCK. Fix it, rescan, get SHIP.
A report from the product
This is a capture of the Sekrd report UI for sekrd.com. The score in the image is from that capture.
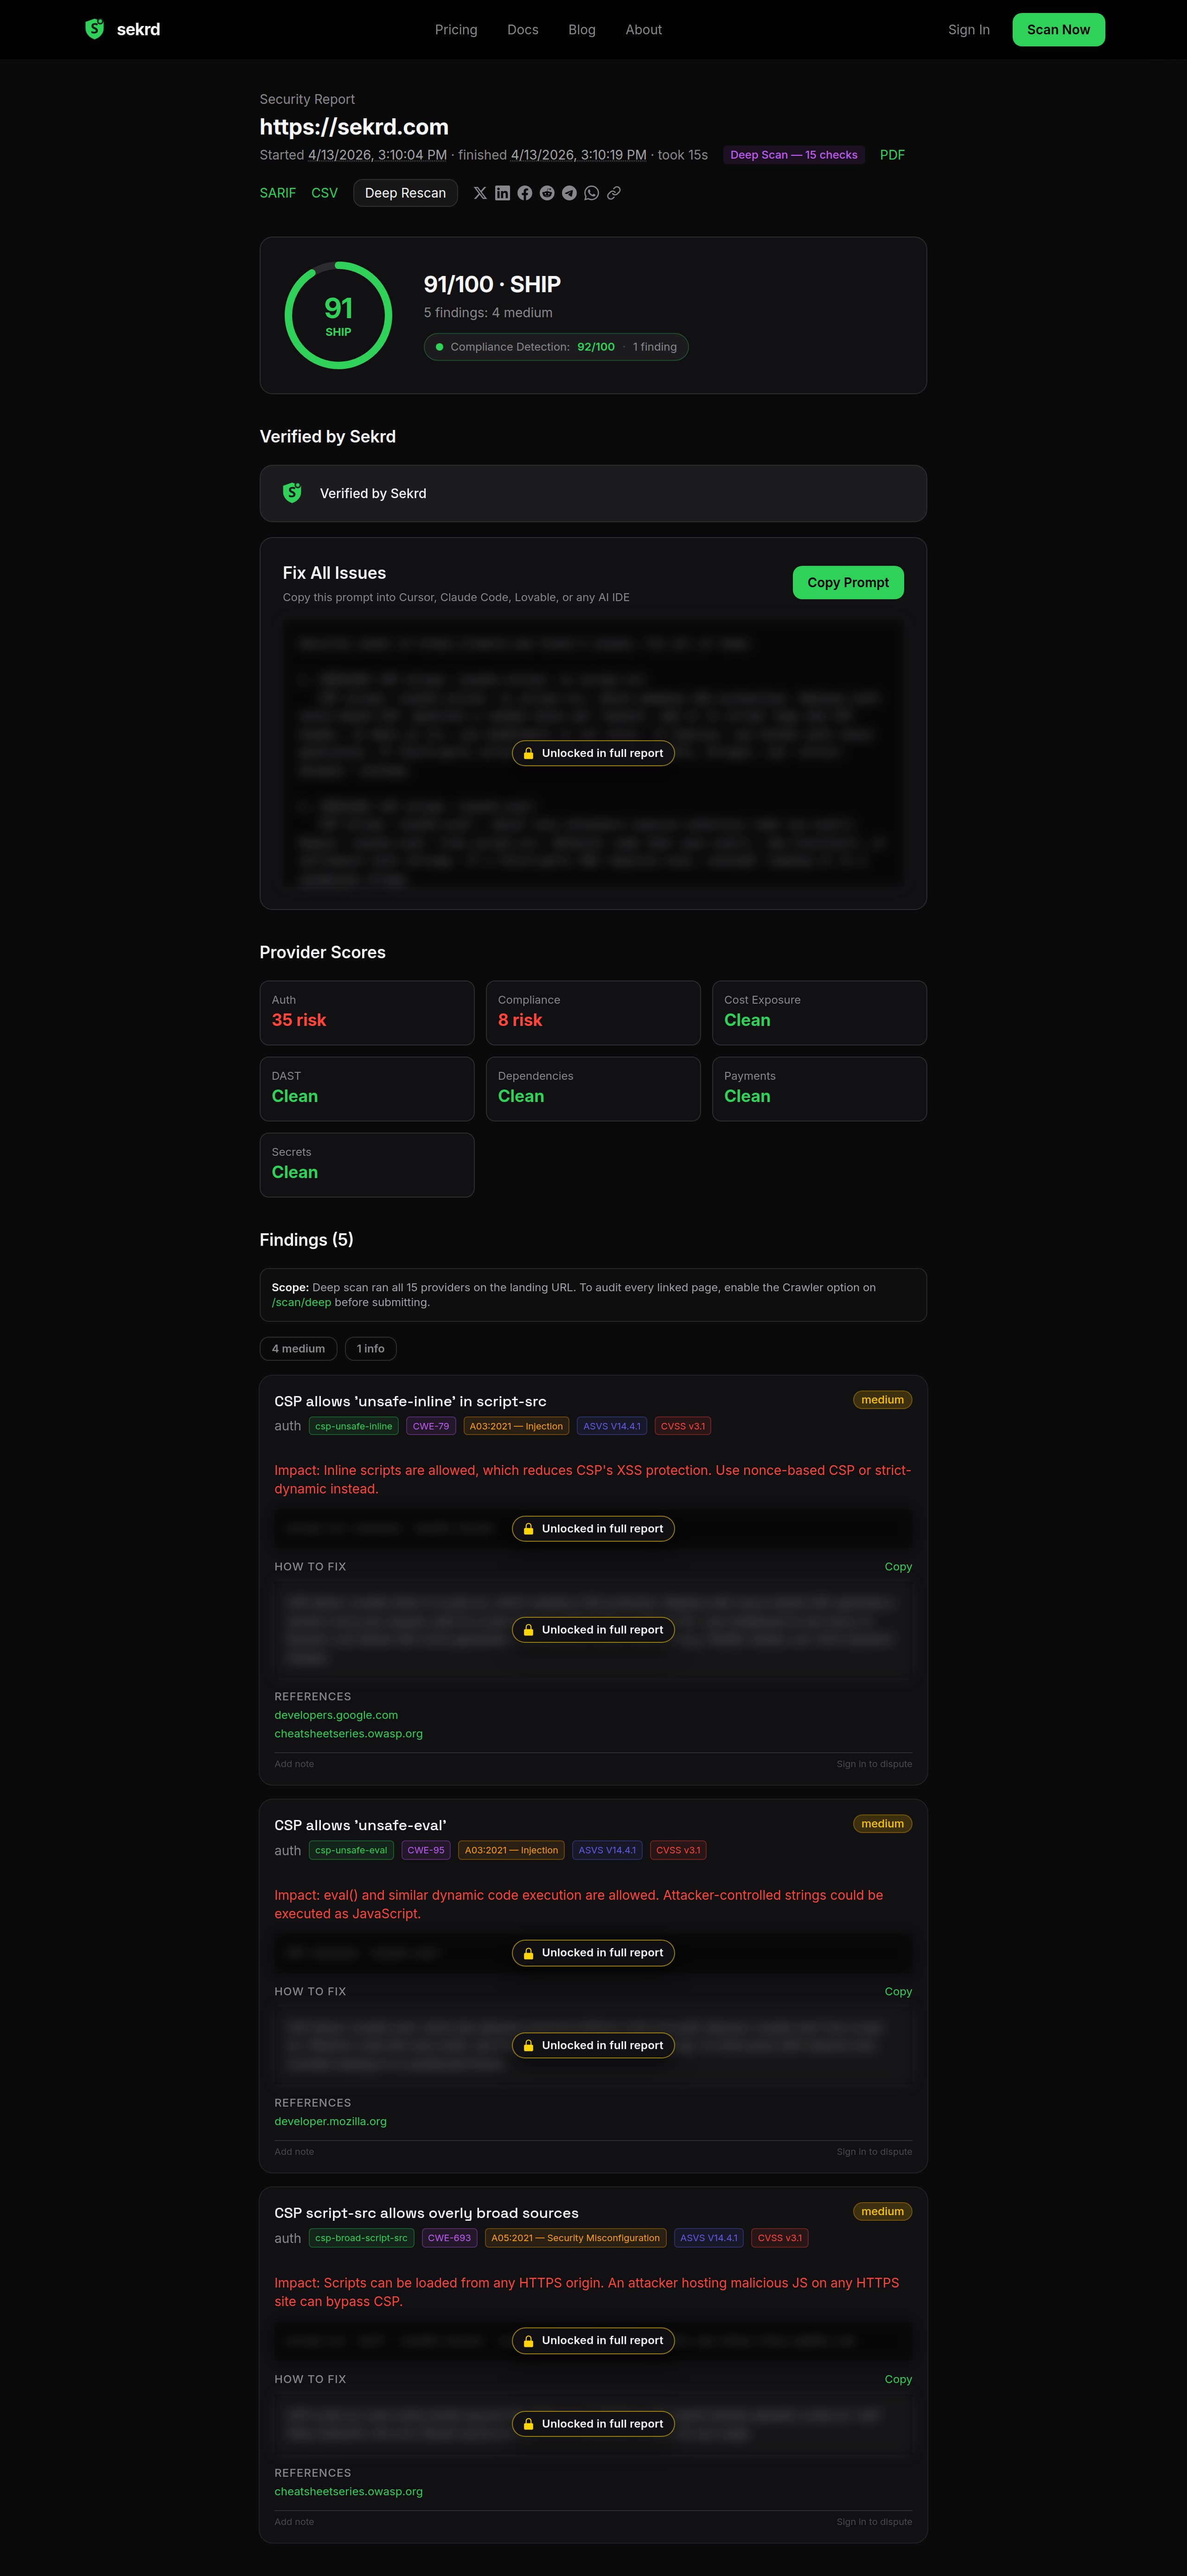

Live badge for sekrd.com. It follows the latest scan of this site.
Your data stays yours
We know you're trusting us with access to your backend. Here's how we handle it.
Read-only access
We never modify your database, RLS policies, or security rules. Strictly read-only audit.
Credentials secured
Credentials kept during your plan period for re-scans, then auto-deleted. Delete anytime from settings.
Encrypted in transit
All data transmitted over HTTPS/TLS. Scans run in isolated environments.
Works with your stack
Pricing
Don't ship until you're sekrd.
Start free. Pay once for launch. Stay covered with continuous.
Free
Quick check before you ship
- ✓ 5 scans/day signed in (90/mo) · 3/day anon
- ✓ Security score (0–100) and a Ship/Block verdict
- ✓ Anonymous: one finding with description and impact, and a locked fix prompt. A URL-only scan cannot see RLS policies such as USING (true)
- ✓ Signed in: the rest of scans you own, including evidence and fix prompts
- ✓ Sekrd Verified badge if you pass
- ✓ Telegram /scan command
- ✓MCP server for Cursor and Claude Code. Install from source in that public repo. Not published on npm.
Pre-Launch Audit
Ship with confidence
$39 once, not $29/month.
- ✓ Everything in Free, plus:
- ✓ Deep scan: all 15 checks (RLS, DAST, OSV CVE, secrets...)
- ✓ Full findings with file paths + line numbers, including checks a URL scan skips
- ✓ Fix prompts on those deep-scan findings
- ✓ Compliance mapping: GDPR / CCPA / Apple Privacy Manifest / Google Data Safety / EU AI Act
- ✓ Generated privacy policy + ToS templates
- ✓ App Store + Google Play submission checklists
- ✓ Site Crawler — full attack surface
- ✓ PDF report (App Store, due diligence)
- ✓ 7 days of unlimited re-scans
One-time. No subscription. Pay once, scan freely for 7 days.
Continuous Pro
Sleep at night
$288/year (save $60)
- ✓ Everything in Pre-Launch, plus:
- ✓ Daily automated re-scans
- ✓ Drift alerts: new CVE, new endpoint, TLS expiring
- ✓ Compliance drift monitoring
- ✓ Vercel Deploy Gate — auto-block bad deploys
- ✓ GitHub Action included
- ✓ Telegram + email alerts
- ✓ Monthly compliance status PDF
Cancel anytime.